





Blog post
2 mins
Trusted by

Security & availability

Information security

Data protection
Healthcare data

California privacy
Artificial Intelligence

Application usage and switching patterns.
Time allocation by process and task type.
Workflow sequences and decision paths.
Process variants and exception paths.
Application names and interaction metadata.
Data security
All data encrypted in transit using TLS 1.2+, and at rest using AES-256. Keys are managed to industry best practice and rotated regularly.
Role-based access controls throughout, with no standing privileged access. Every access request is time-limited, logged and reviewable.

Hosted on enterprise-grade cloud infrastructure, with each customer in a private environment. Penetration tested regularly by independent third parties.
Continuous monitoring, regular patching and a responsible disclosure program. Security incidents follow a defined response protocol, with customer notification SLAs built in.

Certifications and compliance
Certifications
Independently audited annually for security, availability, and confidentiality by an accredited third party.
The international standard for information security management. Certified by an accredited third-party body.
The international standard for AI management systems. Certified by an accredited third-party body.
Regulatory Frameworks

Built to comply with the EU's General Data Protection Regulation. Lawful basis, data minimisation and the right to erasure are all built into the platform.

California Consumer Privacy Act compliance for customers operating in California or with California-resident data.
HIPAA-ready for healthcare deployments. PCI-aware for financial services. The platform supports the frameworks that govern your industry.
Privacy

Data minimization
Skan AI captures only what's needed to model how work happens. Data is retained only as long as its stated purpose requires.Right to erasure
Individual data can be deleted on request, with a full audit of what's been captured, retained and removed. Yours to inspect at any time.Retention controls
Customer-defined retention periods for every category of captured data, with automated deletion the moment a retention period expires.Whitelist controls
Customers control which applications are observed and which are excluded. Personal apps, sensitive systems, anything off-limits. Set the rules, and Skan AI respects them.AI ethics
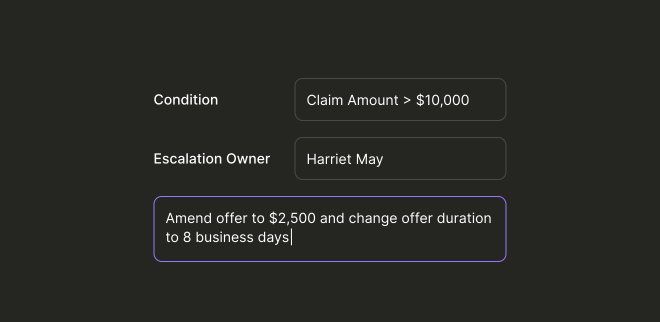
Skan AI supports human decision-making, not autonomous decision-making. Recommendations are always reviewed and approved by experts.
Every recommendation is traceable back to the data behind it, so teams can understand why it was made and review the supporting context.

Models and recommendations are regularly reviewed and tested to identify potential bias across workflows, teams and operational environments.
Customers control how Skan AI is deployed within their organization, including communication, governance and operational policies.
Skan AI is designed to prioritize operational patterns over individual monitoring, with controls that support anonymity, data minimization and restricted access.
Workplace observation platforms should capture operational patterns such as application usage, workflow sequences, process steps and time allocation. They should avoid capturing personal messages, passwords, keystrokes or business content.
They can protect sensitive data through encryption, access controls, masking, redaction, retention policies and customer-controlled observation settings.
Companies should focus on workflow patterns, process performance and team-level operational insights rather than individual monitoring. The goal should be improving how work gets done, not evaluating individual employees.
Common standards include SOC 2 Type II, ISO 27001, GDPR, CCPA and industry-specific requirements for regulated sectors such as financial services and healthcare.
